

Fortinet FortiGate 31G Firewall in Kuwait City, Kuwait
The Fortinet FortiGate 31G is a compact security appliance for businesses that want firewall control, secure VPN, SD-WAN, application visibility and FortiGuard service options in a practical desktop form factor. It is particularly well suited to small offices and branch environments where secure internet access, manageable policy control and local logging matter. FourTeck helps Kuwait buyers review firewall sizing, FortiCare and FortiGuard bundles, deployment requirements and compatible switching before quotation.
Quick Product Information
Fortinet
FortiGate 31G / FG-31G
Next-generation firewall
30 GB onboard
4 x GE RJ45 network ports
Not provided on standard FG-31G
Small offices, branches and distributed sites
Configuration and supplier dependent
Product Overview
FortiGate 31G is designed for organizations that need a manageable security gateway without the footprint or interface density of a larger enterprise appliance. It sits naturally at the internet edge of a small office, retail branch, clinic, school administration site, warehouse office or professional-services location. From that position it can apply firewall policy, network address translation, application-aware controls, intrusion prevention, malware inspection, web filtering and secure VPN functions according to the FortiGuard subscriptions selected by the buyer. The platform also includes SD-WAN capabilities through FortiOS, allowing organizations to use routing and link-steering policies when more than one WAN path is available.
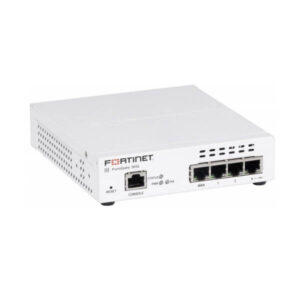
The distinguishing hardware point of the FG-31G is its 30 GB onboard storage. Compared with a model that has no integrated storage, this can be useful for businesses that want a local repository for logs and operational data within the capabilities of the appliance. It does not replace a dedicated long-term logging or analytics platform for environments with large retention requirements, but it gives smaller deployments a practical additional resource. Fortinet specifies four Gigabit Ethernet network ports in the family: one GE WAN, two GE RJ45 ports and one GE RJ45 FortiLink port by default. A separate RJ45 console port is provided for management.
Performance should always be interpreted against the security services that will actually be enabled. Fortinet lists up to 4 Gbps firewall throughput for the 30G family, while enterprise-mix IPS throughput is up to 800 Mbps, NGFW throughput up to 570 Mbps and threat-protection throughput up to 500 Mbps. Those figures are useful for sizing, but real performance depends on packet sizes, traffic mix, enabled inspection, logging, VPN use and policy design. FourTeck therefore recommends selecting the appliance by workload rather than by the highest headline number alone.
For Kuwait businesses, the practical purchasing question is usually not simply whether the unit is fast enough. Buyers should also confirm user count, internet bandwidth, SSL inspection plans, number of VPN users, site-to-site tunnel requirements, VLAN segmentation, logging expectations, subscription term, support coverage and future growth. FourTeck can review those items before quotation so the requested bundle is aligned with the business environment.
Key Business Benefits
Unified Edge Security
Firewalling, VPN, routing, SD-WAN and subscription-based threat controls can be managed from one FortiOS appliance, reducing the number of separate boxes a small site needs to operate.
Local Log Capacity
The 30 GB internal storage gives the 31G an advantage for deployments that want local logging capacity as part of the firewall design, subject to retention and policy requirements.
Branch Connectivity
IPsec VPN and SD-WAN capabilities support secure connectivity between a branch, head office, cloud environment or other business location when designed with the correct policies.
Compact Deployment
The desktop form factor is easy to position in smaller IT rooms, reception back offices and branch cabinets where a full rack firewall may be unnecessary.
Fortinet Ecosystem Fit
A FortiLink-capable port allows the firewall to participate in Fortinet access-layer designs with suitable FortiSwitch equipment, helping centralize policy and visibility.
Practical Upgrade Path
Organizations can size subscriptions, logging, switching and wireless around the branch requirement and move to a larger FortiGate model when users, WAN speed or inspection demand grows.
These benefits are most useful when the firewall is purchased as part of a complete network plan. A small security appliance can perform very well in its intended role, but it still needs correctly designed policies, up-to-date security services, appropriate switching and an internet connection that matches the business requirement. FourTeck can help customers translate a technical wish list into a procurement-ready configuration.
Product Highlights
- Four Gigabit Ethernet network interfaces: suitable for WAN, LAN and FortiLink-oriented branch designs.
- 30 GB onboard storage: differentiates the 31G from the 30G base model and supports local logging use cases.
- FortiOS platform: brings firewall policy, VPN, routing, SD-WAN and security-service integration into one management environment.
- Threat inspection options: IPS, application control, malware protection and web-security functions are available according to the selected FortiGuard services.
- High-availability support: Fortinet specifies active-passive and active-active HA configurations for the family; deployment design and licensing should be reviewed before purchase.
- Compact desktop chassis: useful for branches and small environments where space is limited.
- Trusted Platform Module: hardware-backed cryptographic functions support platform security.
A key buying clarification is PoE. The standard FG-31G does not provide PoE output on its network ports. If the project needs to power FortiAP access points, IP phones, cameras or other powered devices, include a compatible PoE switch or choose a Fortinet model specifically offered with PoE interfaces. This distinction matters because a firewall with a FortiLink port can manage or integrate with access-layer equipment without itself supplying electrical power to endpoint devices.
Technical Specifications
Specification figures are useful for comparing models, but they are not a substitute for sizing. A firewall processing plain traffic behaves differently from one performing IPS, application control, malware inspection, SSL inspection and extensive logging at the same time. When asking FourTeck for a quotation, share your internet speed, approximate user count, expected VPN usage, number of VLANs, branch links, required FortiGuard services and whether centralized logging is planned. Those details help determine whether the 31G is appropriate or whether moving to a larger FortiGate family would provide more operational headroom.
Configuration and Buyer Guidance
Start with the workload. Count users, not only computers: phones, tablets, guest devices, cloud services, VPN sessions, CCTV management stations and IoT endpoints can all generate traffic and policy requirements. Then look at internet bandwidth. If the office has a modest WAN circuit and needs web filtering, IPS, application control and a limited number of VPN tunnels, the 31G may fit well. If the site has very high-speed internet, heavy encrypted inspection or many simultaneous remote users, choose based on inspected throughput and growth rather than raw firewall throughput.
Estimate peak concurrent users and the number of endpoints behind the firewall.
Match WAN speed to the security services you plan to enable, especially SSL inspection.
Confirm FortiCare and FortiGuard term, bundle contents and renewal expectations before ordering.
Plan a PoE switch if powered APs, phones or cameras are part of the project because the FG-31G itself does not supply PoE.
Also decide whether the onboard storage is enough for your logging objective. Local logs can be convenient for branch troubleshooting, but organizations with audit, compliance or longer retention requirements may need FortiAnalyzer, FortiGate Cloud or another supported logging approach. If the firewall will be installed in a cabinet, confirm ventilation, power, UPS protection and cable management. If the deployment replaces an existing firewall, prepare current WAN details, VLANs, routes, VPN peers and policy requirements before migration.
Ideal Business Use Cases
Small Office Internet Edge
Apply policy, web controls, application rules and threat inspection to staff internet traffic in a compact office network.
Branch-to-Head-Office VPN
Connect a branch securely to a head office or hosted environment using site-to-site IPsec VPN with suitable routing and policy design.
Dual-WAN Branch
Use secure SD-WAN capabilities for policy-based path selection and improved control when more than one internet service is available.
Retail or Clinic Network
Separate business systems, staff devices and guest access using VLANs and firewall policy, with appropriate switching behind the appliance.
Fortinet Access-Layer Integration
Use FortiLink with compatible FortiSwitch infrastructure for a more integrated branch design while keeping PoE supply at the switch layer.
Local Logging Requirement
Use the 31G variant when internal storage is desirable for branch logging and troubleshooting within the limits of the 30 GB capacity.
Each scenario depends on the enabled services and deployment scale. A ten-user professional office with one internet line has a different traffic profile from a busy retail branch with guest Wi-Fi, cloud POS, cameras and multiple VPN peers. FourTeck can help convert the real environment into a model and license recommendation rather than assuming that every branch needs the same firewall configuration.
End-User Buying Guide and Practical Product Questions
A firewall purchase works best when the buyer begins with the network requirement rather than the product name. FortiGate 31G for business use is aimed at smaller and distributed sites that need more than basic NAT and port blocking. It can provide policy-based internet access, VPN, application visibility, secure SD-WAN and subscription-driven threat protection, but the actual result depends on licensing, configuration and the surrounding network. Before placing an order, write down how many people use the site, which cloud applications matter, the WAN speed, whether remote access is required and which internal networks need separation.
One common question is whether the model is suitable for a particular number of users. There is no single correct user-count figure because ten users transferring large files through encrypted inspection can create more demand than fifty users doing light browsing and email. A better sizing method combines internet bandwidth, enabled security profiles, VPN load, session count, web application mix and future growth. For this reason, customers researching FortiGate 31G specifications should pay particular attention to the 500 Mbps threat-protection and 570 Mbps NGFW performance figures rather than relying only on the 4 Gbps firewall headline.
Configuration is the next purchasing decision. The hardware model is only one part of the order. Buyers should confirm the FortiCare support level and FortiGuard security bundle required for the desired protection services. If the business needs IPS, anti-malware, web filtering, application control and other subscription services, the quotation should state the bundle and term clearly. A one-year and three-year project can have very different commercial implications, and renewal planning should be considered before deployment rather than at the end of the first term.
Compatibility also extends beyond licensing. The FG-31G includes Gigabit Ethernet interfaces, so existing switch uplinks, VLAN design and WAN handoff should be checked. If a business expects the firewall to power wireless access points or IP phones directly, this model is the wrong assumption: the standard unit has no PoE output. A compatible PoE switch should be included for powered devices. The FortiLink port can be used in Fortinet access-layer designs, but FortiLink is a management and integration function, not a source of PoE power by itself.
Installation planning should cover placement, power and cabling. The appliance is compact and desktop oriented, with an optional wall-mount approach, but it still requires ventilation and stable power. In offices where internet and VPN uptime are important, placing the firewall and access switch on an appropriate UPS can help protect against short power interruptions. Cable labels, documented WAN settings and a written port map make later support much easier. If the 31G is replacing another firewall, migration should capture current address objects, NAT rules, VPN details, routes and critical exceptions so the cutover does not depend on memory.
Before Ordering
Confirm WAN speed, user count, required security services, VPN needs, VLANs, support term and switch requirements.
For Daily Use
Plan policy ownership, log review, configuration backups, firmware maintenance and renewal responsibility.
For Growth
Allow headroom for faster internet, more users, additional branches, deeper inspection and new cloud applications.
For PoE Devices
Specify a compatible PoE switch or another firewall model with explicit PoE capability; do not assume the 31G powers endpoints.
Warranty and support details deserve the same attention as hardware. Ask what FortiCare level is included, the support term, replacement conditions and the process for handling a hardware issue. Subscription and warranty coverage can differ between a bare appliance and a bundled SKU. Procurement teams should keep the exact SKU on the purchase order so renewal and asset records remain clear.
When an exact model is unavailable, the correct alternative depends on why the 31G was selected. If onboard storage is important, consider another FortiGate variant with integrated storage. If more inspected throughput is needed, move to a larger model family. If PoE is a hard requirement, compare a model that explicitly provides PoE interfaces or combine the firewall with a FortiSwitch PoE model. Alternatives should be selected by workload and architecture rather than by model number alone.
What to Send FourTeck for an Accurate Quote
Share the required quantity, number of users, internet speed, current firewall model, VPN requirement, FortiGuard services needed, preferred support term, branch count, VLAN or segmentation needs, PoE device count, desired logging approach and delivery location in Kuwait. For a replacement project, include the current subscription status and any migration deadline. This information helps FourTeck prepare a cleaner hardware-and-license quotation and identify accessories or alternative models before the order is placed.
FortiGate 31G Secure SD-WAN and VPN
Secure SD-WAN is valuable when a branch needs more intelligent use of WAN connections than simple static routing. FortiOS can combine security policy and path selection so traffic can be steered according to link health and application requirements. In a small branch, this may support primary and secondary internet links, cloud application traffic and site-to-site connectivity without adding a separate SD-WAN appliance. The design still needs correct monitoring targets, routing, failover behavior and application policies.
VPN is equally important for distributed companies. IPsec can connect the branch to a head office, data center or cloud network, while remote-access choices depend on the organization’s security architecture and current Fortinet capabilities. Buyers should define how many people will connect remotely, whether multi-factor authentication is required and whether VPN traffic must pass through additional inspection. The quoted hardware can only be judged properly when those requirements are known.
For Kuwait organizations operating several smaller sites, a standardized branch design can simplify support. Using a consistent firewall family, naming convention, VPN template and logging policy reduces troubleshooting time. FourTeck can help customers prepare model and license requirements for one location or a multi-unit project, while the customer’s IT team or implementation partner can align configuration with the wider network policy.
FortiGate 31G Threat Control and Local Logging
Modern firewalls are purchased for inspected traffic, not merely for packet forwarding. With suitable FortiGuard services, the platform can apply intrusion prevention, malware protection, application control and web security policies. These functions help a business reduce exposure to unwanted applications, suspicious traffic and known threats, but they need deliberate configuration. Turning on every feature with default settings is not a substitute for understanding the network.
The 30 GB internal storage is useful because logs provide context when troubleshooting blocked applications, VPN issues or policy behavior. A small branch can benefit from local visibility, especially when administrators need to review recent events. However, storage capacity, retention period and compliance expectations should be assessed together. High-volume environments may require centralized logging so data is retained longer and analyzed across multiple devices.
During buying discussions, specify whether the organization already uses FortiAnalyzer, FortiManager, FortiGate Cloud or another approved operational platform. Existing Fortinet tooling can influence the most efficient deployment method. FourTeck can help identify the hardware, subscription and support components needed for the intended design, while final security policy should follow the organization’s governance and risk requirements.
FortiGate 31G FortiLink and Access-Layer Planning
The FortiLink-capable interface is relevant for businesses that want closer integration between the firewall and compatible FortiSwitch access equipment. This can simplify certain network-management tasks and help the firewall participate in a broader Fortinet Security Fabric design. It is particularly useful when a branch wants centralized visibility across security and switching rather than managing every component as an isolated device.
The key distinction is power delivery. FortiLink does not mean PoE. A Wi-Fi access point, IP phone or surveillance camera still needs electrical power from a PoE switch or separate injector if the endpoint supports it. For an office with several FortiAPs, phones and cameras, the PoE switch should be sized by both port count and watt budget. This is a common area where a low-cost quotation can become incomplete if powered-device requirements are discovered after the firewall is purchased.
Cabling also matters. Verify that copper links are suitable for Gigabit Ethernet, that patch panels are documented and that uplink design leaves room for segmentation. If the site has more devices than the firewall’s direct ports can accommodate, the normal approach is to use a managed access switch and carry VLANs between the firewall and switch. FourTeck can include switching options in the quotation when customers provide endpoint counts and PoE requirements.
What Buyers Should Check Before Purchase
A correct firewall order includes more than a model code. Buyers should confirm the exact hardware SKU, license bundle, support term, deployment environment and required accessories before approval. The 31G is a storage-equipped compact firewall, so it is a good fit when local logging and a small footprint are important. It should not be purchased on the assumption that its Ethernet ports provide PoE.
Configuration Fit
Compare inspected throughput with actual WAN speed, peak traffic, VPN use and expected growth. Choose the security bundle by services required.
Compatibility Check
Verify switch uplinks, VLAN design, WAN handoff, power, UPS, logging platform and whether PoE endpoints require a separate switch.
Availability and Warranty
Ask for the exact SKU, FortiCare term, FortiGuard bundle, replacement conditions and current supplier availability.
Quote Preparation
Provide quantity, users, bandwidth, VPN count, services, project date and delivery location so the quotation can be matched to the real requirement.
Long-term cost includes renewals, support, operational management and any dependent switching or logging platform. A hardware-only price can look attractive while omitting services necessary for the intended security policy. Conversely, some businesses may not need the broadest security bundle. FourTeck can help review the balance between required services and lifecycle expectations so procurement compares like-for-like configurations.
Kuwait Availability and Service Support
FourTeck supports product inquiries across Kuwait City and Kuwait with assistance for model selection, FortiCare and FortiGuard bundle review, quote preparation, delivery coordination and warranty guidance. Availability may vary by hardware SKU, subscription term, quantity and supplier status, so customers should request a current quotation rather than rely on an old online listing.
For new installations, provide internet bandwidth, user count, VPN requirements and the planned access switch. For replacement projects, include the existing firewall model, current support status and any migration deadline. FourTeck can also help buyers identify whether a PoE switch, UPS or larger FortiGate model should be included in the project. Final installation and security policy should match the customer’s IT standards and operational requirements.
Kuwait City and Area Coverage
Businesses in Kuwait City, Hawalli, Salmiya, Farwaniya, Ahmadi, Jahra, Salwa, Fahaheel, Mangaf, Shuwaikh, Al Rai and other Kuwait locations can contact FourTeck for firewall availability, configuration guidance and quotation support. A branch office in a commercial district may need a simple single-WAN design, while a warehouse or larger professional office may require dual-WAN, VLAN segmentation, site-to-site VPN and PoE switching. FourTeck can review these differences before the order is finalized.
Delivery coordination depends on quantity, supplier status and destination. Customers planning multiple sites should provide a location list and required quantity per site so hardware, subscriptions and accessories can be organized consistently. This is particularly useful when a company wants standardized security policy and support terms across several Kuwait branches.
Kuwait Commercial-Area Availability
Commercial firewall projects frequently involve more than a single appliance. A retail site may also need PoE switching and wireless access points; a professional office may need secure remote access; a warehouse may need network separation for CCTV and operational systems. FourTeck can coordinate product selection and quotation around the complete requirement instead of treating the firewall as an isolated purchase.
Current availability, delivery options, warranty handling and support terms can change with the selected Fortinet SKU and quantity. Buyers should therefore request an updated commercial offer that identifies the exact appliance, FortiCare term, FortiGuard bundle and any accessories. Visit FourTeck Kuwait for business IT product paths or use the FourTeck contact page to send the project requirement.
Other Fortinet Options Buyers May Consider
Alternative models are useful when the project needs a different performance level, more interfaces or a different balance of storage and access-layer requirements. The right choice depends on workload and architecture rather than a simple higher-or-lower model number.
FortiGate 30G
Suitable for similar compact branch use when onboard storage is not required.
FortiGate 50G
Consider for a step up in performance and branch capability when the workload is beyond entry-level needs.
FortiGate 51G
A storage-equipped option in the 50G family for buyers who want more performance headroom and local storage.
FortiGate 70G
Useful when a branch needs more capacity, interfaces or future expansion than the 30G family provides.
FortiGate 71G
Storage-equipped 70G-family option for environments that need higher branch performance with onboard storage.
Why Buyers Choose FourTeck
Help translating project requirements into specific hardware, subscription and accessory items.
Pre-sales discussion around users, bandwidth, VPN, logging, switching and deployment fit.
Commercial quotations based on current requested quantity, bundle and support term.
Coordination according to supplier availability, project quantity and business location.
Help understanding support coverage and the importance of exact SKU and term documentation.
Support identifying PoE switches, UPS protection and larger firewall alternatives when needed.
FourTeck’s role is to help make the purchasing discussion clearer. For a firewall project, that means separating hardware capability from subscription services, understanding where PoE belongs in the topology, checking whether the selected model has enough inspected-throughput headroom and preparing the quotation around the actual deployment rather than only the appliance name.
Frequently Asked Questions
It is a compact next-generation firewall for protecting small offices and branches. Typical uses include secure internet access, firewall policy, IPsec VPN, SD-WAN, application control, intrusion prevention and web-security services when the appropriate FortiGuard subscriptions are active. The 31G also includes 30 GB of onboard storage for local logging and operational data.
No. The standard FG-31G provides Gigabit Ethernet network interfaces but does not supply PoE power to connected devices. If your project includes access points, IP phones or cameras that need PoE, plan a compatible PoE switch or select another Fortinet model that explicitly provides PoE interfaces.
FourTeck supports Kuwait enquiries and can prepare a current quotation based on the requested hardware SKU, FortiCare and FortiGuard bundle, quantity and delivery requirement. Availability changes with supplier status and configuration, so buyers should request an updated quote instead of relying on an older stock statement.
The key hardware difference is onboard storage. The FG-31G includes 30 GB of integrated storage, while the FG-30G base model does not. Network interfaces and core family positioning are closely related, so buyers mainly choose the 31G when local storage is useful for logging and operations.
Yes. Bundle selection should follow the security services the business actually plans to use. Share whether you require IPS, malware protection, web filtering, application control, cloud management or other services, along with the preferred support term, and FourTeck can help prepare the relevant quotation options.
Use inspected-throughput figures rather than only raw firewall throughput. Consider WAN speed, SSL inspection, IPS, application control, VPN traffic, logging and growth. A business with heavy encrypted traffic can need more headroom than another site with the same number of users but lighter applications.
Yes. FortiGate supports IPsec VPN for branch-to-branch and branch-to-head-office designs. The final design should confirm tunnel count, routing, authentication, internet bandwidth and security policy. For larger multi-site environments, centralized management and logging may also be worth considering.
Send quantity, number of users, internet speed, current firewall model, required VPN connections, desired security services, support term, PoE device count, logging requirement and delivery location. For a replacement, include current subscription status and the planned migration date.
Yes. For project or bulk supply, provide the number of locations, quantity per site, desired subscription term and whether the same configuration will be used everywhere. Standardizing SKUs, support terms and accessories can simplify procurement, asset tracking and future renewal management.
The FortiGate 30G is relevant when onboard storage is not required. FortiGate 50G or 51G can suit buyers who need more branch performance, while 70G or 71G may be appropriate for larger requirements. If PoE output is mandatory, use a compatible PoE switch or evaluate a Fortinet model specifically designed with PoE interfaces.
Need Help Choosing the Right Firewall?
FourTeck can help review FortiGate availability, FortiGuard and FortiCare options, PoE switching requirements, warranty guidance and delivery requirements for your Kuwait business location. Send your user count, internet speed, VPN requirement and preferred support term for a more accurate quotation.

Reviews
There are no reviews yet.